 Malcolm Keith 2026
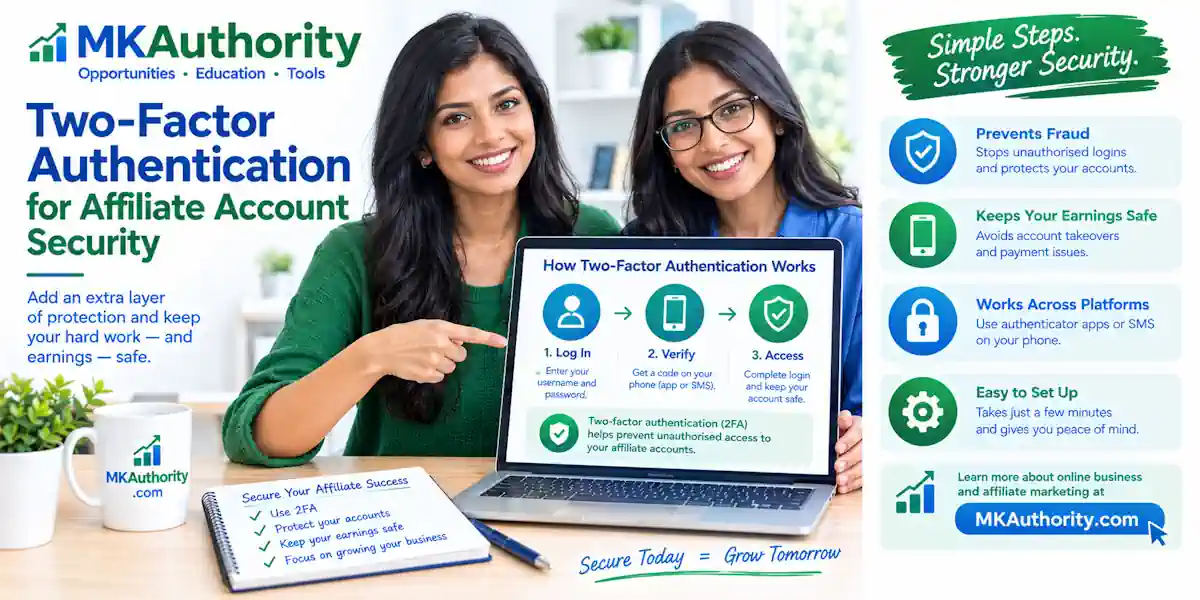

Two-factor authentication (2FA) adds a second identity check to your login, so a stolen password alone usually won’t unlock your affiliate website. Start with your email and administrator accounts, then protect hosting, domains, and commission dashboards.
You don’t need a complicated security setup to make progress. Two-factor authentication works best alongside strong, unique logins, separate credentials, and a recovery plan that works when your phone doesn’t. Let’s start with what that second login step does.
Key Takeaways
- Use a security key or passkey where available, with an authenticator app as a practical alternative.
- Protect every account that can reset access, change affiliate links, or redirect payouts.
- Save recovery codes securely before you need them, and keep tested website backups.
How Two-Factor Authentication Works
Two-factor authentication, or 2FA, requires exactly two distinct authentication factors. Multi-factor authentication, or MFA, is the broader term for using two or more.
The three categories are something you know, such as a password or PIN; something you have, such as a phone or security key; and something you are, such as biometrics, a fingerprint, face, or voice.
A security question doesn’t count as a second factor because it also relies on something you know.
For your affiliate business, that extra factor helps stop reused credentials, credential stuffing, and automated guessing attacks from becoming account takeovers. Give every account a unique password stored in a password manager, too. Reusing them creates trouble across accounts.
Choose the Right Authentication Method
My recommendation is simple: choose phishing-resistant protection when it’s available. Otherwise, an authenticator app is a good starting point.
Here’s how the common options compare.
| Method | Main advantage | Main weakness |
|---|---|---|
| Security key or passkey | Resists fake login pages | Needs a recovery plan |
| Authenticator app | Generates codes offline | Codes can be phished |
| Push approval | Quick sign-in confirmation | Fraudulent prompts can fool users |
| SMS or email code | Easy to enable | Depends on phone-number or inbox security |
SMS and email codes are often six digits, although lengths vary. Criminals can intercept SMS through SIM swaps, where they take over your number. Email codes depend on keeping your inbox secure.
Authenticator apps make a practical starting point
Google Authenticator, Microsoft Authenticator, and Duo support TOTP. TOTP is a time-based one-time password that works without a network connection once configured.
Most codes refresh every 30 seconds; some systems use 60-second windows. Enter the current code before its timer expires.
The FTC’s authentication guidance explains that an authenticator app isn’t vulnerable to SIM swaps. However, a fake login page can still steal a code you type into it.
Security keys and passkeys resist phishing
USB and NFC security keys use cryptographic proof tied to the legitimate website. The FTC describes a security key as the strongest 2FA method because it doesn’t expose credentials attackers can steal through ordinary phishing.
A passkey uses related technology and is often unlocked with your device PIN or biometrics. It can replace both the password and separate code.
Passkeys are convenient, but recovery still matters. Register a spare key or another supported recovery method before relying on one device.
Protect More Than Your WordPress Login
Your website has several doors. Locking the CMS dashboard helps, but an attacker could still reset access through email or change settings with your hosting provider or domain registrar.
Start with the email account that receives password resets. Then protect your CMS, hosting provider, domain registrar, affiliate networks, payment services, and email-marketing platform. Turn on 2FA, also called multi-factor authentication (MFA), for accounts that can reset access or redirect income.
Why include affiliate dashboards? Someone who gets in may change payout details without touching your articles.
Give each account its own password. Enable security alerts so unexpected logins and payment changes don’t sit unnoticed.
Subscriber information deserves protection as well. My guide to affiliate data privacy covers why tracking records and contact details need careful handling.
Set Up Two-Factor Authentication on WordPress
For a self-hosted WordPress site, an authentication plugin gives you a practical way to add the second step. The free Two-Factor plugin supports authenticator codes and backup verification codes.
Install, connect, and test your authenticator
Keep your existing administrator session open while setting things up.
- Open Plugins > Add New Plugin, search for Two-Factor, then install and activate it.
- Open Users > Profile and find the two-factor options.
- Enable 2FA with time-based authentication, scan the displayed QR code with an authenticator app, and enter its current code.
- Create backup codes, store them securely, and test a fresh login in a private browser window before closing your existing session.
Treat the QR code and setup secret like credentials. Anyone holding them could generate matching codes.
Control administrator access
Every administrator needs an individual account and a unique password. Don’t share one login with a writer, assistant, or developer.
Use Editor or Author permissions when someone only needs to publish content. Reserve Administrator access for people who genuinely need installation, settings, and user-management powers.
For teams, use a solution that can enforce 2FA by role. Per-user enrollment alone doesn’t guarantee everyone enables it.
Remove unused accounts and end temporary access when the work is finished. Fewer administrator accounts mean fewer high-value logins to protect.
Turn On Google 2-Step Verification
If Gmail receives your business password resets, protect it early with Google 2-Step Verification, Google’s form of 2FA.
Open your Google Account, select Security & sign-in, then find How you sign in to Google. Select Turn on 2-Step Verification and follow the prompts.
Google’s setup instructions cover the available methods. Some device-based methods may use biometrics through your screen lock. Add your preferred method and save recovery options before signing out.
Google prompts let you approve or reject a sign-in with Yes or No. Android phones need updated Google Play services. Only approve a request you started yourself.
A newly added verification phone number can take up to seven days to become trusted. Google may disable a suspicious new number and allow 30 days to confirm it.
So, don’t replace every recovery method at once. Keep working access available while you complete the change.
Build Your Recovery Plan Before Losing Access
Account recovery deserves the same attention as the login itself. Otherwise, one broken phone can interrupt publishing, campaigns, and commission management.
Store backup codes outside your phone
Google backup codes contain eight digits, and each works once. You can print or download them, although accounts enrolled in Advanced Protection can’t download backup codes.
Keep a printed copy of your backup codes somewhere secure or use an encrypted vault you can access independently. Don’t leave your only copy inside the account you’re trying to recover.
When moving phones, transfer your authenticator accounts and test them before erasing the old device. Replace any backup codes you’ve used or exposed.
Close weak recovery routes
Account recovery can bypass the normal second-factor challenge, so 2FA recovery routes need protection. An attacker may target an old recovery email, an insecure phone number, or guessable security answers.
Secure recovery email accounts with their own unique passwords and 2FA. Remove obsolete recovery details, and store random security-question answers in your password manager. Each answer is still “something you know,” so don’t use easy-to-guess details.
Keep hosting recovery instructions outside WordPress. Google’s recovery guidance also explains alternatives when your usual second step isn’t available.
Understand What 2FA Cannot Stop
Two-factor authentication reduces account-takeover risk, but it doesn’t eliminate credential stuffing. It won’t repair vulnerable plugins, remove malware, or protect a stolen browser session.
Watch for fake prompts and recovery abuse
A push notification can become an attack route. IBM describes MFA fatigue attacks, in which criminals send repeated approval requests until someone accepts one.
Reject unexpected prompts. Open the account directly instead of following links in alarming security messages. IBM’s phishing-resistant MFA explanation describes why cryptographic methods resist attacks that ordinary codes cannot.
Keep WordPress, themes, plugins, and devices updated. Maintain a WordPress backup plan for files and the database, with copies outside your hosting account under separate credentials. Test restoration before trouble arrives.
Payment requirements have their own scope
NIST’s July 2016 draft proposed deprecating SMS authentication. Its 2017 final guidance retained phone-network authentication as restricted, rather than treating it as a preferred option.
Payment compliance rules also have their own scope. Older PCI DSS versions placed remote-access authentication requirements under 8.3; version 4 uses requirement 8.4.
The EU’s PSD2 strong customer authentication requirement took effect on September 14, 2019, for covered payments, subject to exemptions.
Publishing affiliate links doesn’t automatically give your blog the same obligations as a merchant handling card data.
What to Do If an Account Is Compromised
Act quickly, but use a clean device. Changing passwords on an infected computer can hand the replacement credentials straight back to the attacker.
- Secure your email and account recovery methods, then change affected passwords and revoke active sessions.
- Remove unknown devices, authenticators, passkeys, connected apps, API keys, and administrator accounts.
- Contact your host or account provider through its official support channel. Preserve security alerts and relevant logs.
- Inspect affiliate destinations, redirects, payout details, advertising access, and email automations for unauthorized changes.
If website files were altered, close the entry point, then clean the site or restore a known-clean backup. Restoring files alone doesn’t remove an attacker’s account access.
If personal information was exposed, address any notification duties that apply.
Frequently Asked Questions
Where do I find my 2FA code?
Open the authenticator app connected to the account and select its entry to see the verification code. SMS and email codes arrive through those channels instead.
Security keys and passkeys usually don’t display a code. Connect the key or approve the device’s authentication request.
What if I lose my phone?
Use a saved backup code, spare security key, or another enrolled method. If none remains, use the provider’s official recovery process.
After regaining access, remove the lost device and replace exposed recovery material. Don’t pay strangers who promise to bypass account security.
Protect the Accounts That Protect Your Income
Start with your email, domain, hosting, and administrator access. Choose the strongest supported method, then make sure you can recover without your everyday phone.
The goal is reliable control over your website, subscribers, and commission accounts. Two-factor authentication helps protect that control when you combine it with unique passwords, limited access, updates, and tested backups.