 Malcolm Keith 2026
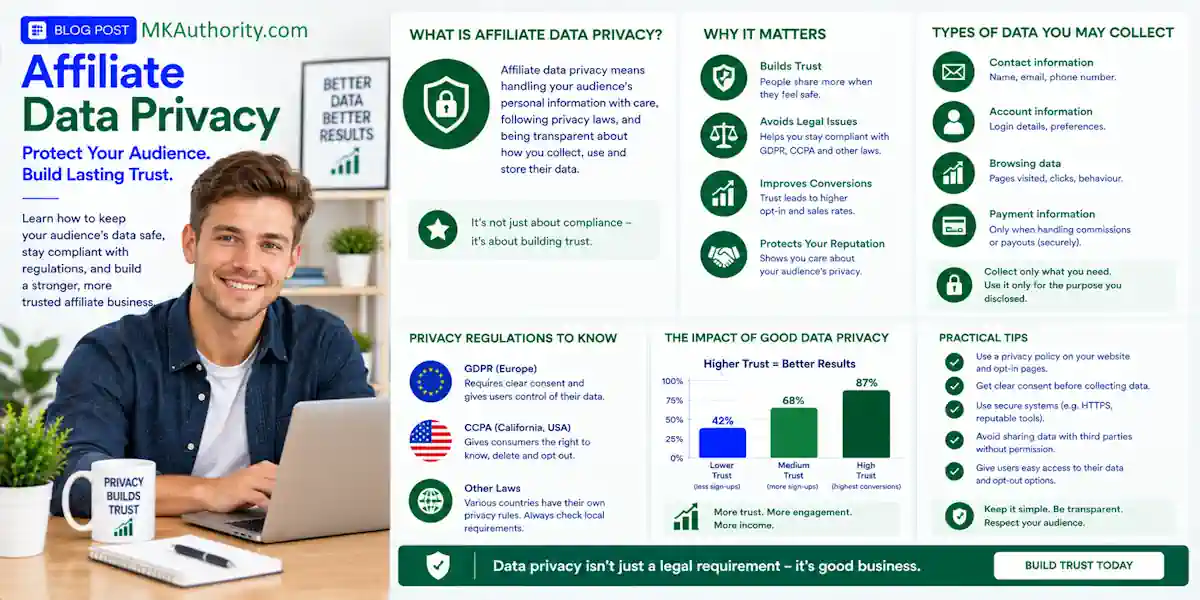

A single affiliate link can trigger more data collection than most beginners realize. Affiliate data privacy covers click IDs, cookies, analytics tags, pixels, redirects, email signups, conversion reports, and usage data connected to that link.
That doesn’t mean you should stop tracking. It means tracking with your eyes open, keeping data lean, and explaining what happens before a browser starts doing the work.
This guide covers practical privacy best practices and legal requirements, which vary by jurisdiction, without turning your small website into a legal maze.
Key Takeaways on Affiliate Data Privacy
- Affiliate links can involve personal information even when you never see a visitor’s full name.
- Cookie consent, a privacy notice, a disclosure, and an opt-out are four different things.
- Browser pixels help with affiliate attribution, but server-side postbacks are usually stronger for confirmed conversions.
- First-party data collected directly from visitors still needs a reason for collection, a clear notice, security, retention limits, and a way to handle valid requests.
- Your SubIDs should identify campaigns and placements, never people.
Why affiliate conversion tracking creates privacy risk
Affiliate marketing isn’t only about sending someone from your review page to a merchant. The path often includes a tracking URL, an affiliate network redirect, browser storage, analytics software, ad-platform tags, and a merchant-side conversion report.
A click ID may look harmless, but affiliate attribution can connect its referral to a conversion. Analytics may also associate usage data with a device or user profile, making the activity personal information.
Affiliate data privacy involves the information your setup may collect
You might collect data directly through forms, or indirectly through tags and reports. The basic question is simple: can this setup identify someone, single out their device, or connect activity back to them?
| Tracking item | Common affiliate use | Affiliate data privacy concern |
|---|---|---|
| Click ID | Matches a referral to a conversion | Can link activity across pages or systems |
| Cookie or local storage | Remembers a referral or consent choice | Often needs consent in EU and UK contexts |
| IP address | Security, logs, analytics | May be personal data |
| Email address | Lead magnets and newsletters | Needs notice, security, and deletion handling |
| SubID | Identifies ad, page, button, or email | Dangerous if it contains customer details |
The safer approach is simple. Track the campaign, page, placement, and creative identifiers. Don’t put names, email addresses, phone numbers, or customer records into tracking parameters. This guide to privacy-safe affiliate SubID tracking shows how much useful reporting you can get without exposing people.
Accuracy and compliance are separate jobs
A setup can report every sale and still break privacy rules. Another setup can have a perfect cookie banner but lose half its tracking because redirects or click IDs fail.
You need both: accurate reporting for good decisions and required consent controls for legal obligations. Data minimization is a risk-reduction best practice.
The financial stakes are real. The CMS GDPR Enforcement Tracker reported about EUR6.11 billion in GDPR fines by March 1, 2026. That total isn’t a prediction of what a small blogger will pay. It’s a reminder that data rules aren’t optional paperwork.
How EU and UK rules affect affiliate data privacy
The GDPR, or general data protection regulation, can apply when people in the European Economic Area are involved. That includes businesses outside Europe offering services or monitoring their behavior. The eprivacy directive supports the EU framework, while the UK GDPR and PECR create similar concerns for UK visitors.
Your location isn’t the only factor. These data protection laws may depend on visitor location, your purpose, and how you collect usage data.
Cookies, pixels, redirects, and link decoration
Affiliate tracking cookies aren’t usually “strictly necessary” just because you want commission credit. Browser-based affiliate tracking can involve third-party cookies, tracking pixels, scripts, browser storage, fingerprinting methods, and URL parameters. Cookie deprecation can change attribution, but it doesn’t remove privacy obligations.
The UK’s Information Commissioner’s Office explains that PECR reflects the eprivacy directive. Consent depends on the tool, purpose, visitor location, and applicable jurisdiction. Users must be told about cookies and similar tools, why they’re used, and must actively agree where required. Review the ICO cookie guidance before assuming your affiliate tag is exempt.
Pre-ticked boxes, silence, or “keep browsing to accept” are weak choices for consent. A visitor needs to give unambiguous consent through a clear affirmative choice, not assumed agreement.
The narrow exception is not a shortcut
Some loyalty or cashback services may argue that affiliate tracking is part of a service the user directly requested. This narrow exception is fact-specific, not a general exemption.
That argument does not automatically cover a normal product review, comparison page, bridge page, or paid ad funnel.
If you are earning a commission from a standard affiliate click, treat the tracking as non-essential unless qualified legal advice tells you otherwise. You will find a plain-English explanation in this affiliate cookie consent overview.
US privacy rules are different, not absent
The United States doesn’t have one GDPR-style federal privacy law for every small website. Instead, its consumer privacy framework combines state laws, sector rules, consumer protection laws, and changing thresholds. Unlike the EU and UK, the U.S. approach relies heavily on state-by-state data protection laws.
The California Consumer Privacy Act (CCPA) and CPRA are the names most marketers know. They may apply when a business meets specific coverage thresholds or engages in covered activities. California’s adjusted civil penalty can reach $7,988 for an intentional violation or a violation involving a consumer known to be under 16. Check the California Privacy Protection Agency’s penalty adjustment rather than relying on old blog posts.
Opt-out rights can affect affiliate vendors
If a covered business “sells” or “shares” personal information under California statutory definitions, it may need a clearly labeled opt-out option. It must honor valid opt-out signals, while broader privacy controls remain a best practice.
The global privacy control, often called GPC, is one browser-level signal you may need to recognize. Your affiliate network, CRM, analytics vendor, ad platform, and email provider all matter here.
Don’t assume that being small makes every state rule disappear. For legal compliance, check where you do business and who you target. Review your data collection and whether partners use it for their own purposes.
Consent, privacy notices, disclosures, and opt-outs
These items get mixed together all the time. They should not be mixed together.
Cookie consent controls the tracking action
Consent is permission before non-essential cookies, pixels, or similar tools run, where the law requires it. In Europe, the eprivacy directive and national implementation shape many cookie requirements.
A consent management platform, or CMP, should block those tags until the visitor makes an active choice. That choice should amount to unambiguous consent when consent is the required legal basis.
Google Consent Mode can adjust how Google tags behave after a visitor grants or denies consent. That can help with tag control and measurement settings. It doesn’t create consent or replace a proper banner or privacy notice.
Your cookie policy for affiliate websites should name the categories you use, explain their purpose, and tell people how to change their choice.
A privacy notice explains the full data picture
Your privacy policy should explain what you collect, why you collect it, who receives it, how long you keep it, and how people can ask about their data. It should also cover contact forms, email lists, analytics, comments, security logs, and affiliate tracking where relevant.
A good privacy policy for affiliate websites isn’t a magic shield. It should match what your site really does. If the policy says one thing and your tags do another, the policy loses its value fast.
An ftc disclosure explains your commission relationship
An ftc disclosure tells readers you may earn money if they buy. It’s an advertising-transparency requirement, not a substitute for privacy consent.
Place the ftc disclosure before, or right beside, your first affiliate link or recommendation. A normal sentence works well: “This post contains affiliate links. If you buy through one, I may earn a commission at no extra cost to you.”
Use clear FTC affiliate disclosure examples in digital marketing, including blog posts, emails, video descriptions, and social promotions. A footer link or a disclosure page alone isn’t enough when the recommendation appears somewhere else.
A reader can agree to cookies and still not know you earn a commission. A reader can see your disclosure and still have the right to refuse marketing cookies.
Build a CMP and server-side tracking setup
This is where things get practical. Don’t start by adding more tools. Start by mapping what you already have.
Inventory every tracking handoff
Open your website, tag manager, affiliate network dashboard, link tracker, email platform, CRM, and ad accounts. Include tracking cookies and tracking pixels in your inventory, alongside every tag, redirect, webhook, and postback.
Flag third-party cookies and vendor-controlled scripts as separate handoffs.
For each one, record:
- What data it receives and sends.
- Why you need it.
- Whether it runs before consent.
- Which company receives the data.
- How long the data remains available, including its data retention period.
- Whether you have data processing agreements or a similar contract with the vendor.
The ICO’s broader guidance on storage and access technologies is useful here because it covers more than old-fashioned cookies. Pixels, link decoration, device fingerprinting, and scripts can also create privacy duties.
Blocking tags and logging consent are compliance controls. Tag inventories and vendor reviews are best practices that help demonstrate accountability.
Block first, then fire conditionally
Set your consent management platform (CMP) to load essential functions first. Hold back non-essential analytics, ad pixels, retargeting scripts, and affiliate tags for visitors in regions where consent is required.
Then connect each consent category to the tags it controls. Test all three paths, confirming unambiguous consent where required:
- The visitor accepts tracking.
- The visitor rejects tracking.
- The visitor changes their mind later.
Make sure a refusal actually prevents the tag from firing. Keep those tags blocked until consent is valid where required, and make withdrawal stop future tracking. Keep a consent record that shows the choice, date, privacy policy version, and categories selected.
Use first-party data and postbacks carefully
First-party data is information your site collects directly. It can include email subscribers, form submissions, purchase history, and usage data, such as pages someone viewed on your site.
Zero-party data is information people deliberately give you, such as a survey answer, preferred training topic, or request for beginner affiliate tools. It is often more useful because the person chose to provide it.
First-party does not mean free to collect
You still need a clear reason to collect first-party data directly. Apply data minimization and ask for only what you need. If a free checklist only needs an email address, don’t demand a phone number, job title, income, and location too.
Keep data retention periods sensible. Remove inactive leads when you no longer have a valid reason to keep them. If you use hashed emails for ad measurement, remember that hashing changes the format, not your responsibility to protect personal information.
For lighter site measurement, consider privacy-focused Google Analytics alternatives that may collect less visitor-level information than a typical ad-heavy setup.
Server-side tracking improves confirmation
A browser pixel fires when the visitor’s browser loads code, often on a thank-you page. It can miss events because of browser restrictions, ad blockers, script errors, cross-device journeys, or a dropped cookie.
A server-to-server postback works differently. The merchant, network, or advertiser’s server sends a confirmed conversion event to your tracker or affiliate platform. Server-side tracking is usually the stronger source for affiliate attribution, including approved leads, sales, rebills, refunds, reversals, and cleared commissions.
Still, this method is not a privacy loophole and doesn’t override consent, privacy notices, security, retention, or vendor obligations. A click ID can remain personal data if it links back to a person or device. Use short-lived IDs, pass only necessary fields, secure the endpoint, and document the vendor relationship.
Handle access and deletion requests without panic
If someone asks what data you hold about them, don’t search one spreadsheet and hope for the best. A proper data subject access request, or DSAR, often touches several systems.
Verify the request and find the records
First, verify the person’s identity in a sensible, proportionate way. Don’t demand more information than needed, but don’t hand personal data to the wrong person either.
Search the email platform, form tool, CRM, ecommerce records, help desk, analytics account, link tracker, affiliate network reports, and server logs for relevant usage data. Match records using the email address or another legitimate identifier.
Under GDPR, organizations generally need to respond within one month, while California has different timing and verification rules. These processes aren’t identical. Response periods vary by jurisdiction and may change in special situations, so get legal guidance if the request is complex.
Send deletion requests to vendors too
Deleting a lead in your email tool doesn’t automatically erase it from your CRM, webinar platform, affiliate tracker, or backup schedule. Your vendor list should tell you where to send each follow-up request.
Keep a simple central log for each data subject access request as a best practice. Record the request date, identity checks, systems searched, vendor confirmations, actions taken, and response date. That record protects the visitor and gives you a clear process next time.
Stop fraud without collecting everything
Privacy-friendly tracking doesn’t mean blind tracking. You still need to spot cookie stuffing, forced clicks, fake leads, spoofed referrals, trademark bidding, and duplicate conversions.
Watch for patterns, not personal profiles
Cookie stuffing happens when someone drops affiliate cookies without a genuine referral click. Forced clicks can open redirects or trigger links without a clear user action. Both can produce junk reporting and broken trust.
Look for sudden click spikes, impossible conversion timing, repeated device signals, unusual traffic sources, or many conversions from the same placement with little engagement. Limited usage data can reveal these patterns without creating detailed personal profiles. Review suspicious activity manually and document partner checks before making accusations.
Protect your links and conversion events
Give important buttons their own campaign-level identifiers. Your hero button, comparison-table link, and final call to action shouldn’t all use the same label.
Use deduplication when both a pixel and a postback can report the same action. One sale should produce one conversion. Also check each program’s rules before using redirects or short links, since affiliate link cloaking rules vary by program. Redirect, cloaking, and tracking requirements can differ between programs.
A practical affiliate data privacy checklist
You don’t need a massive compliance department. You do need a repeatable affiliate marketing compliance routine before launch.
- List every program, tracker, tag, pixel, form, email tool, CRM, and advertising platform connected to the campaign.
- Apply data minimization by removing personal information from SubIDs, URL parameters, and custom conversion fields.
- Add a clear FTC disclosure before the first promotional link, button, or recommendation.
- Update your privacy policy and cookie policy to match the tools that are actually active.
- Use a CMP to block non-essential tags where consent is required, then test acceptance, rejection, and withdrawal paths.
- Set up server-side tracking and postbacks where the network or merchant supports them. Use confirmed conversion data for serious budget decisions.
- Review each affiliate network’s contracts, data processing terms, retention settings, and first-party data handling.
- Create one request workflow for access, correction, deletion, and opt-out demands.
- Test your click path after every major page-builder, redirect, tag-manager, or offer change.
- Review campaign claims, disclosures, tracking rules, and merchant terms for legal compliance before spending money on digital marketing or paid traffic.
This routine isn’t glamorous, but it supports compliance, saves headaches, and isn’t a substitute for jurisdiction-specific legal advice. It also keeps you focused on the numbers that matter, valid leads, approved sales, refunds, reversals, and cleared commissions.
Frequently asked questions on affiliate data privacy
Do affiliate cookies always require consent?
No universal rule covers every country or affiliate program, because data protection laws vary by country and state.
In the EU and UK, affiliate cookies will often need affirmative, unambiguous consent under the general data protection regulation and the eprivacy directive. Those cookies support tracking and attribution, rather than a service the visitor directly requested.
A narrow exception can exist in special cashback or loyalty cases. Don’t stretch that exception across ordinary affiliate content without legal advice.
Does server-side tracking avoid GDPR or CCPA rules?
No. Moving measurement to your server reduces dependence on the visitor’s browser, which can improve conversion confirmation. It doesn’t remove duties around notices, consent where required, contracts, security, retention, access requests, or opt-outs.
Treat it as a measurement upgrade, not a compliance escape hatch.
Can I put an affiliate disclosure only in my footer?
No. A footer disclosure may support transparency, but it shouldn’t be your only notice. Readers need to see the commercial relationship before or beside the recommendation and affiliate link.
The same rule matters in promotional emails. Put a clear disclosure in each email that contains an affiliate offer.
What should I do if I am not sure which rules apply?
Start by reducing the data you collect, documenting your tools, and making your notices truthful. For U.S. audiences, review consumer privacy rights, opt-out requirements, and whether your tools honor the global privacy control browser signal.
This FAQ covers common compliance considerations, not a universal legal conclusion, because rules and thresholds vary by jurisdiction. Then speak with a qualified privacy lawyer about legal compliance.
This is especially important if you target EU or UK visitors, run paid traffic at scale, handle sensitive data, use advanced retargeting, or receive a formal data request.
This article is general information, not legal advice. Laws, state thresholds, platform rules, and affiliate program terms can change.
Final Thoughts on Affiliate Data Privacy
Good affiliate data privacy is not about giving up on tracking. It means collecting only first-party data your site needs, getting consent when required, and treating server-confirmed data as risk reduction, not a loophole.
Good affiliate marketing compliance means clean tracking, clear commission disclosures, and attention to obligations that vary by jurisdiction. Visitors know what is happening, which can mean better numbers, stronger trust, and fewer surprises when campaigns make money.
Home Business Academy Funnel Builder